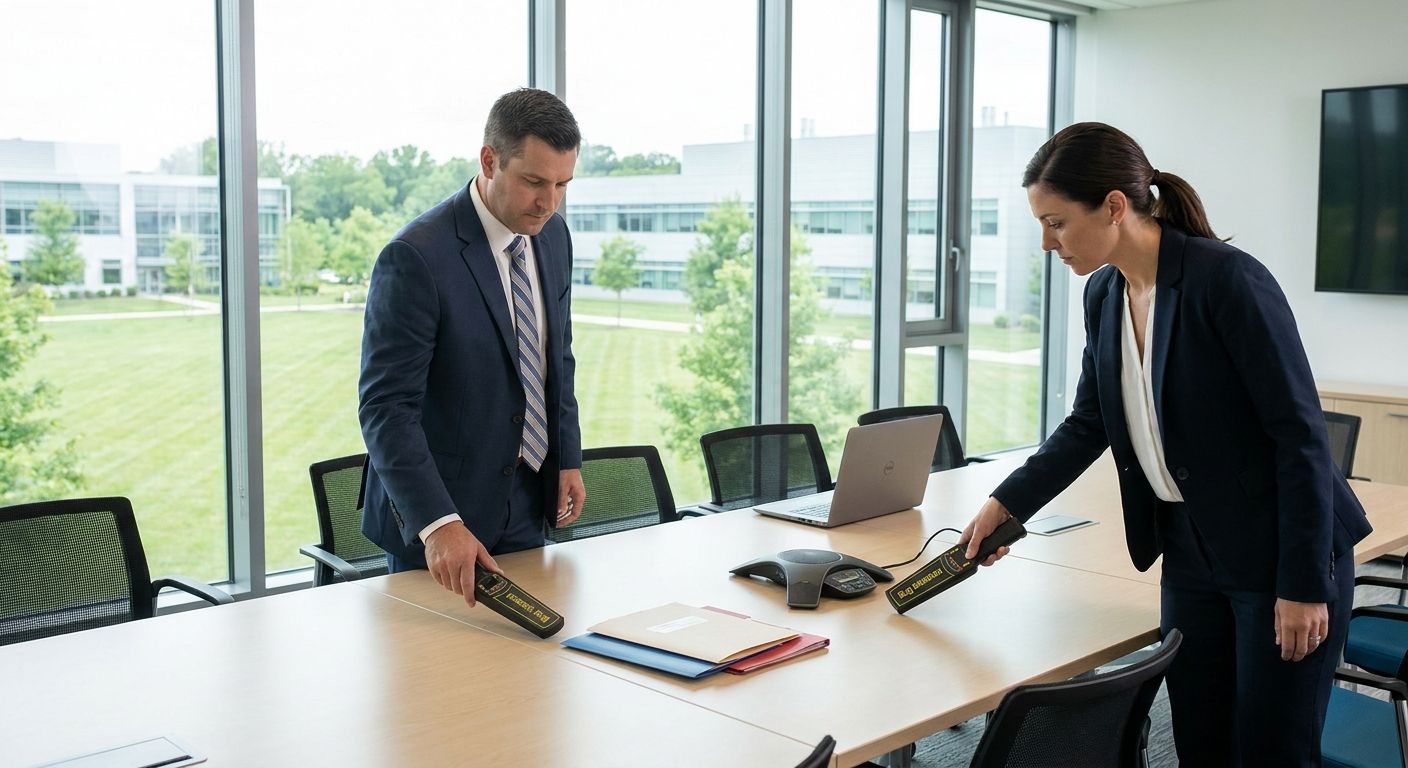
Pharmaceutical and biotech bug sweep services are TSCM (technical surveillance countermeasures) inspections calibrated to protect drug formulas, clinical trial data, and FDA submission timelines from hidden cameras, audio bugs, and RF transmitters planted by competitors or insiders. A pharma company's threat model is different from a retail store or law firm: the assets at risk are unpatented compounds, unpublished trial results, and merger terms worth hundreds of millions of dollars, not just customer records.
That difference changes where you sweep, how often, and what triggers an inspection. A biotech company running Phase III trials has a narrower, higher-value target zone than a general office — the formulation lab, the data room, and the boardroom where licensing deals get negotiated.
- Bug sweep for pharmaceutical companies targets R&D labs, data rooms, and boardrooms — not the whole building.
- USA Bugsweeps runs TSCM inspections before FDA submissions, licensing talks, and Phase III trial readouts.
- Professional RF sweeps scan below 1 MHz up to 6 GHz to catch devices consumer detector apps miss.
- Patent-pending compounds carry 20 years of exclusivity risk — a single leaked formula erases that value overnight.
- Skip 12-month sweep cycles for biotech; tie inspections to your trial calendar and deal timeline instead.
Why bug sweeps matter for pharmaceutical and biotech companies
Pharma and biotech firms sit on information that competitors, short sellers, and foreign state-linked actors actively want before it's public. A leaked Phase III readout can move a stock price days before the official announcement. A stolen formulation can wipe out a 20-year patent window before the product ever ships. This is not a hypothetical risk category — it's the same reasoning driving trade secret protection for tech startups, scaled to an industry where a single compound can represent a decade of R&D spend.
The FDA's Hatch-Waxman framework grants new chemical entities roughly 5 years of market exclusivity on top of patent protection — a window that only holds value if the underlying data stays confidential until the agency clears it. Boardrooms negotiating licensing deals or acquisitions carry the same exposure: term sheets discussed in a conference room become worthless leverage the moment a competitor hears the number first.
A TSCM bug sweep team built for this sector doesn't just check for cameras in a break room. It's built around the calendar events that create the highest risk: pre-submission meetings, trial readouts, and closed-door M&A sessions in 2026.
The bug sweep checklist for pharmaceutical and biotech companies
Map your high-value information zones
Before any sweep happens, identify which rooms actually hold information worth stealing. Not every square foot of a pharma campus carries the same risk.
- Formulation and synthesis labs where compound data is generated
- Data rooms used for due diligence during licensing or acquisition talks
- Executive offices and boardrooms where trial results get discussed pre-announcement
- IT server rooms and network closets tied to clinical trial databases
- Any room used for calls with the FDA or outside counsel
Sweep before major deals and trial announcements
Timing matters more than frequency in this industry. A quarterly sweep schedule misses the actual risk window, which clusters around specific events.
- Schedule an inspection 24-72 hours before signing a licensing agreement
- Sweep the data room before opening it to an acquiring company's diligence team
- Check boardrooms the morning of a Phase II or Phase III readout meeting
- Re-sweep after any contractor, vendor, or temp staff has had unsupervised room access
- Add a sweep to the checklist before earnings calls tied to pipeline updates
Check R&D labs and formulation rooms for RF and lens threats
Labs are harder to sweep than offices — equipment racks, HVAC ducts, and cabinetry all create hiding spots a visual check alone won't catch.
- Run a non-linear junction detector across bench areas and storage cabinets
- Inspect ceiling tiles, vents, and light fixtures for pinhole lens cameras
- Check any device plugged into a wall outlet that doesn't belong to the facility's own equipment list
- Scan for RF transmitters hidden inside spare hardware, extension cords, or power strips
- Flag any USB device, smart speaker, or IoT sensor not on the IT department's approved list
A general security consultant can run a walk-through, but most aren't trained on spectrum analysis or non-linear junction detection — the two techniques that catch devices a visual sweep alone can't find. That's the point where a professional TSCM sweep from USA Bugsweeps becomes the faster, more thorough path rather than a first resort.
Secure boardrooms and executive offices before M&A talks
Boardrooms are the single highest-value room in a pharma company during acquisition season. The same logic applies to corporate boardroom sweeps run for other industries, but the stakes scale with deal size in biotech.
- Sweep the room, not just the table — check chairs, wall art, and AV equipment
- Inspect conference phones and video units for hardware or firmware tampering
- Confirm Wi-Fi access points in the room match the IT department's authorized list
- Check any gift, plant, or decor item introduced by an outside party before the meeting
Schedule a sweep before your next trial readout
TSCM inspections timed to your submission and deal calendar, nationwide.
Screen vehicles and devices of traveling executives
Executives carrying trial data or deal terms on laptops and phones are a mobile risk, not just a stationary one. This mirrors the concerns covered for bug sweep services for executives and public figures, applied to a pharma travel schedule packed with investor meetings and conference appearances.
- Check company vehicles for GPS trackers before and after conference travel
- Inspect laptop bags and hotel rooms during multi-day licensing negotiations
- Confirm phones haven't been physically tampered with after leaving them unattended
- Review hotel conference rooms booked for confidential calls before using them
Protect patient and trial-participant data at the room level
Clinical sites carry patient privacy exposure on top of IP risk. The physical-security angle overlaps closely with medical office bug sweeps, since trial sites are effectively medical offices with an added layer of confidential protocol data.
- Sweep exam and consultation rooms used for trial participant visits
- Check any device left behind by outside monitors or CRO staff
- Confirm recording equipment used for informed-consent documentation is authorized and logged
Build a recurring sweep schedule tied to your development calendar
Once the one-off sweeps are done, put a repeatable schedule in place instead of reacting after a leak.
- Tie sweep frequency to trial phase milestones, not the calendar month
- Re-sweep any room after facility renovations or new furniture installs
- Log every sweep date and findings for internal compliance and insurance records
- Loop in legal counsel on any device found so evidence handling doesn't compromise a future claim
Comparison: sweep options for pharma and biotech companies
| Option | Best For | Key Limitation |
|---|---|---|
| Consumer RF detector app | A quick personal spot-check on a phone | Misses passive recorders and most hidden lenses entirely |
| General security consultancy | Broad physical security audits, guard staffing | Rarely trained in spectrum analysis or non-linear junction detection |
| In-house IT/security team | Ongoing network and cyber monitoring | Not equipped for physical RF sweeps or lens detection |
| Professional TSCM sweep (USA Bugsweeps) | Labs, boardrooms, and executive offices ahead of high-stakes events | Requires scheduling lead time; doesn't replace continuous cyber monitoring |
Verdict: a consumer RF app or a general security guard walk-through is not a substitute for a professional TSCM sweep before a pharma company signs a licensing deal or opens a data room.
Common mistakes pharmaceutical and biotech companies make
- Sweeping the whole campus instead of the high-value rooms. Spreading a limited budget across every office wastes time that should go toward the lab and boardroom.
- Treating cybersecurity as a substitute for physical TSCM. A firewall doesn't catch a pinhole camera in a formulation lab or a recorder taped under a boardroom table.
- Waiting until after a leak to sweep. By the time a competitor announces a suspiciously similar compound, the damage to a 20-year patent window is already done.
- Skipping the sweep after contractor or vendor visits. Anyone with unsupervised access to a lab or data room resets the risk clock, even a trusted long-term vendor.
- Assuming a sweep before an FDA meeting is optional. Pre-submission strategy discussions are exactly the kind of confidential content that draws competitor interest.
FAQ
What is a bug sweep for pharmaceutical companies?
A bug sweep for pharmaceutical companies is a TSCM inspection of labs, boardrooms, and data rooms to detect hidden cameras, audio bugs, and RF transmitters. It focuses on the rooms where trial data, compound formulas, and deal terms get discussed.
How often should biotech companies sweep for hidden devices?
Biotech companies should sweep tied to trial milestones and deal activity, not a fixed calendar. Sweep before FDA submissions, licensing signings, trial readouts, and after any contractor or vendor access to secure rooms.
Can a bug sweep detect corporate espionage in a lab?
A professional TSCM sweep can detect the physical devices used for corporate espionage, including hidden cameras, RF transmitters, and audio bugs planted in lab equipment or fixtures. It does not replace a separate cybersecurity audit of networks and databases.
Is a bug sweep necessary before FDA submissions?
Yes, pre-submission strategy meetings often contain unpublished trial data and regulatory positioning that competitors have financial incentive to hear early. A sweep of the meeting room and any devices used reduces that exposure.
How much does a TSCM sweep cost for a pharmaceutical company?
Cost depends on square footage, number of rooms, and how many devices need inspection, so it varies by facility. Request a quote based on the specific labs, offices, and boardrooms you need covered.
What's the difference between a bug sweep and a cybersecurity audit?
A bug sweep checks for physical surveillance devices like hidden cameras, audio bugs, and GPS trackers in a physical space. A cybersecurity audit examines networks, servers, and software for digital intrusion, and pharma companies typically need both.
Do biotech startups need bug sweeps before board meetings?
Biotech startups negotiating funding rounds or licensing deals in board meetings carry the same espionage risk as larger pharma companies. A sweep before any meeting discussing valuation, IP, or deal terms is a reasonable precaution.
Can hidden GPS trackers be a risk for pharma executives?
Yes, GPS trackers placed on a company vehicle can reveal travel patterns tied to investor meetings, conference attendance, or facility visits. Checking vehicles used by traveling executives is part of a full TSCM program.
One last thing
Most pharma security budgets go entirely toward network firewalls and access badges — and skip the physical layer completely. A formulation lab with a locked door and a badge reader is still exposed if nobody ever checked the vents, the phone system, or the conference room AV unit for a transmitter that's been broadcasting for months. In 2026, the cheapest insurance against a leaked trial result isn't another software license — it's a physical sweep of the three or four rooms where the real decisions get made.